ISO/IEC 27701 · Lead Auditor
ISO/IEC 27701 Lead Auditor: Privacy Information Management System
Gain the skills to plan, conduct and close a privacy information management system audit against ISO/IEC 27701, using widely recognised audit principles and evidence-based technique.
- Trainer-Led
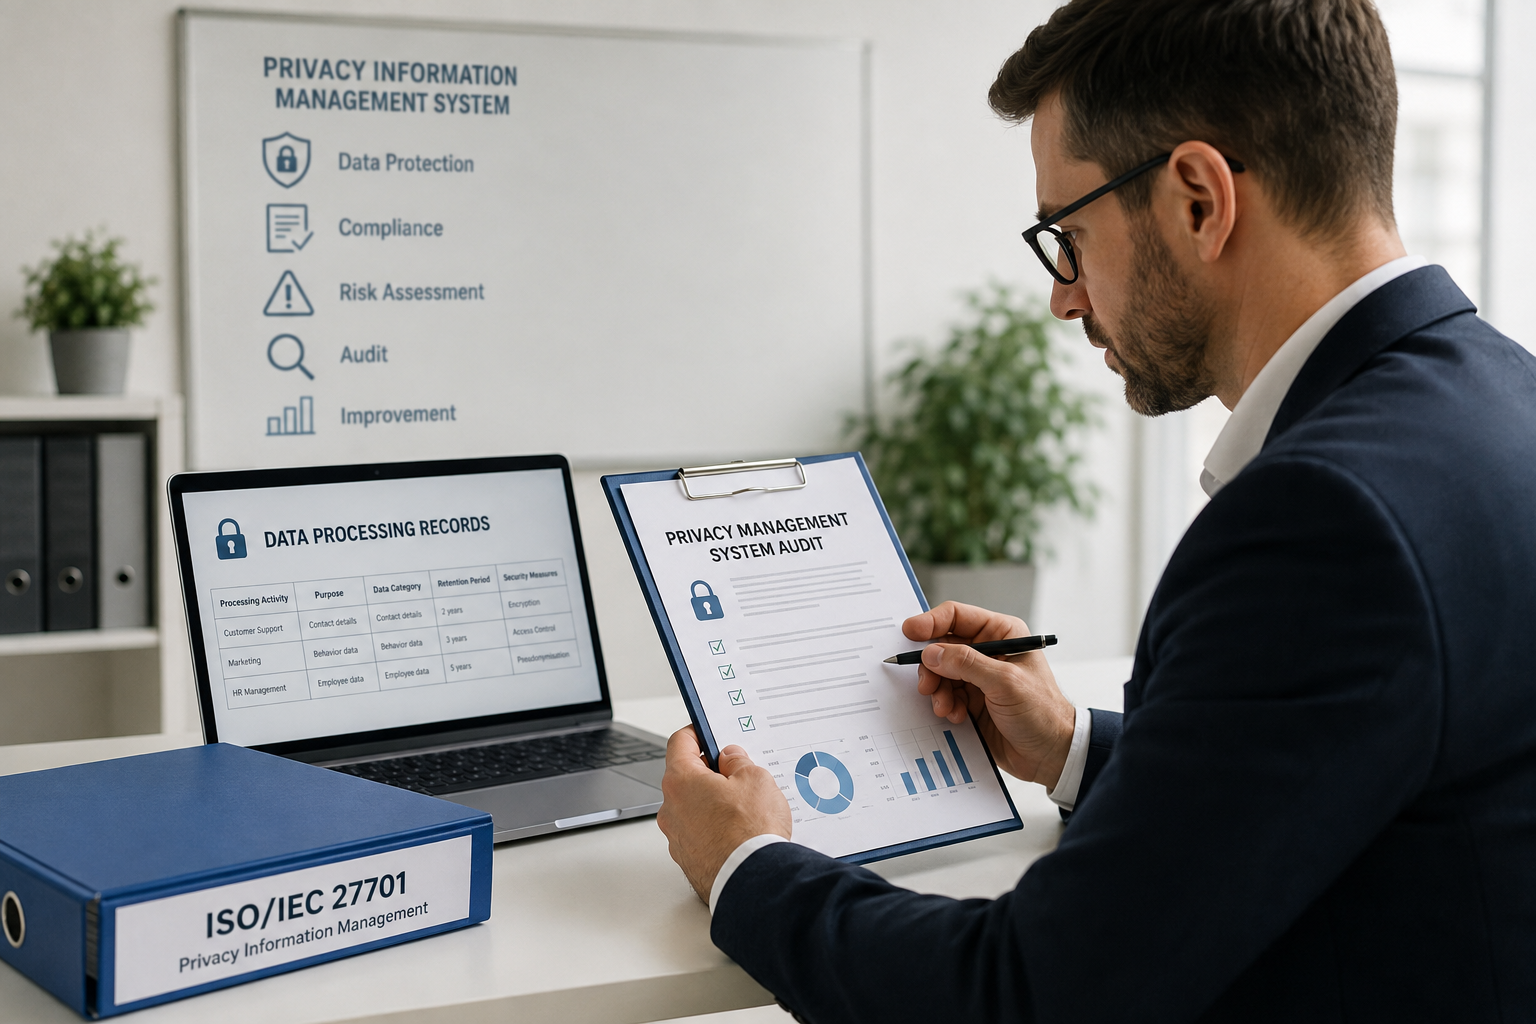
The auditor's perspective
This course teaches you to assess conformity, not build a PIMS from scratch. The emphasis is on evidence: what adequate PII controller or processor documentation looks like, how to test whether a stated data-handling control actually operates, and what constitutes a major nonconformity.
Where this fits
Auditor competence here transfers directly into internal audit programmes and second-party assessments of vendors handling personal data, increasingly requested alongside ISO/IEC 27001 in Australian procurement processes.
What you will learn
- Explain the fundamental concepts and principles of a privacy information management system
- Interpret ISO/IEC 27701 requirements for a PIMS from the perspective of an auditor
- Evaluate PIMS conformity to ISO/IEC 27701 requirements using fundamental audit concepts and principles
- Plan, conduct and close an ISO/IEC 27701 audit in accordance with ISO/IEC 17021-1 and ISO 19011
- Manage an ISO/IEC 27701 audit programme
Course content
1. Introduction to the PIMS and ISO/IEC 27701
Fundamental concepts, ISO/IEC 27701 requirements and the certification process.
2. Audit principles and planning
Fundamental audit concepts, risk- and evidence-based auditing, and initiating the audit.
3. On-site audit activities
Stage 2 audit execution, communication during the audit and audit procedures.
4. Closing the audit
Drafting findings and nonconformity reports, evaluating action plans and managing an audit programme.
Exam and certification
Open-book written exam delivered online through PECB Exams. Duration: 3 hours.
Your fee includes your first exam attempt and one free retake within 12 months. After passing, you can apply for the relevant PECB credential.