
ISO/IEC 27001 · ISO/IEC 27002 · Lead Implementer
ISO/IEC 27001 Lead Implementer: Information Security Management System
Build the theoretical and practical knowledge to implement an ISO/IEC 27001 information security management system and run a risk management process with confidence.
- Self-Paced
- Trainer-Led
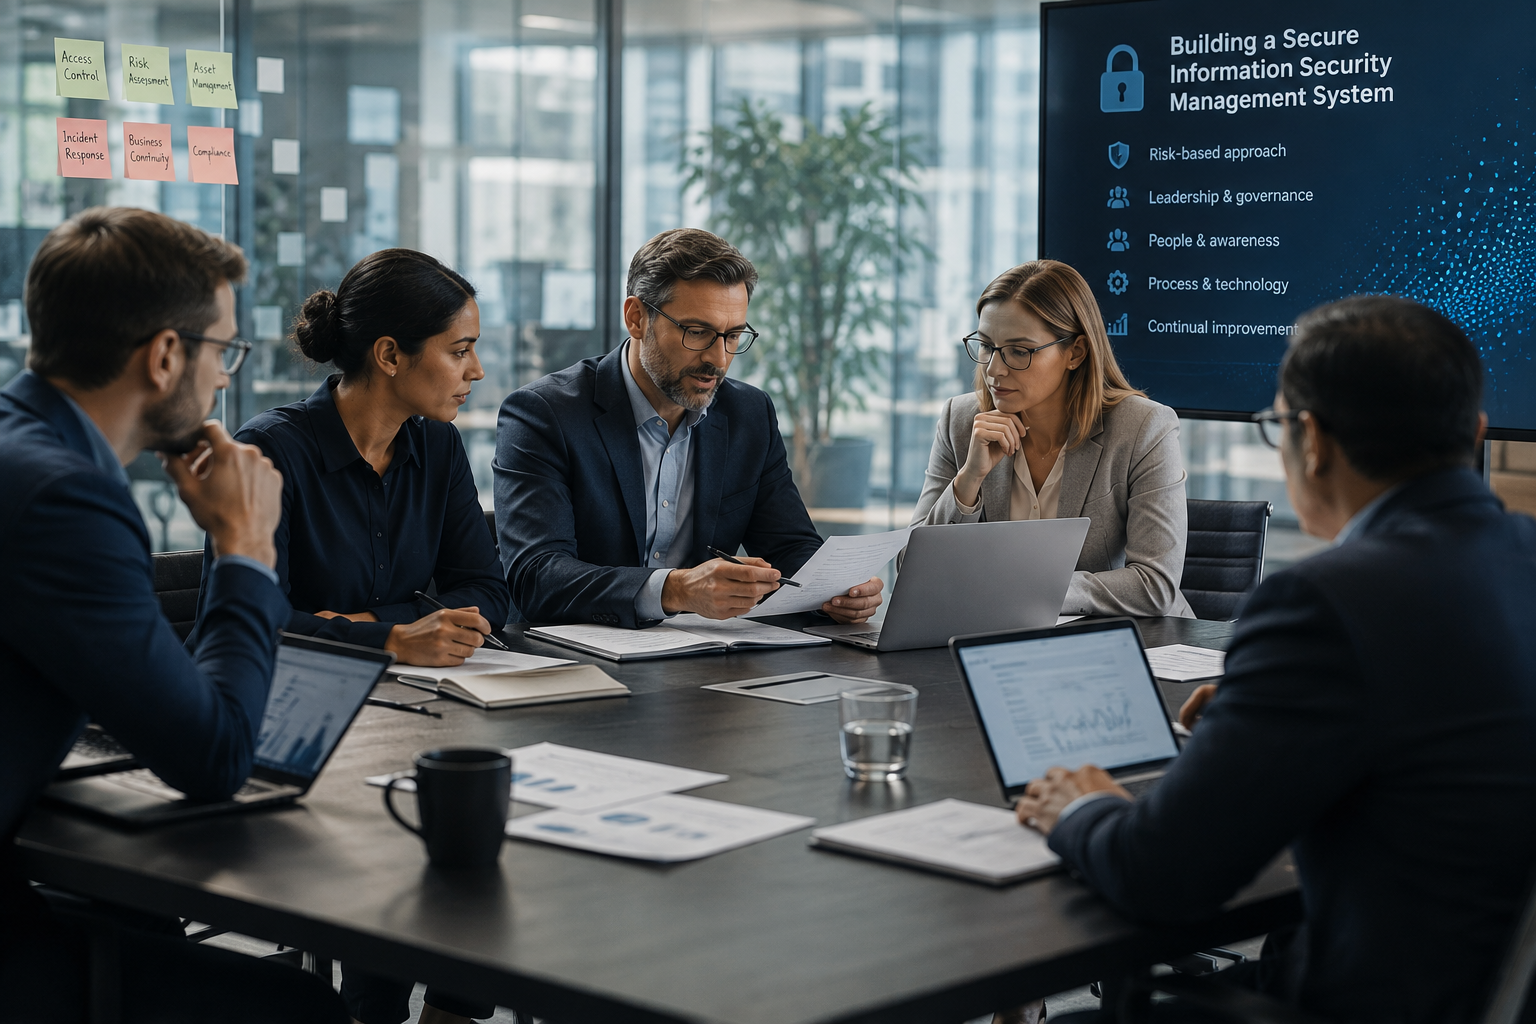
Why ISO/IEC 27001 matters in Australia
ISO/IEC 27001 is the international benchmark for managing information security. Australian organisations increasingly encounter it as a condition of doing business: in government tenders, in supply chain assurance questionnaires, and in contracts with enterprise customers who need assurance that their data is handled properly.
Certification also intersects with obligations under the Privacy Act 1988 and, for many organisations, the Essential Eight and the Notifiable Data Breaches scheme. An ISMS gives you a defensible, documented basis for the security decisions you have made.
What makes the Lead Implementer course different
Foundation-level training explains what the standard says. Lead Implementer training teaches you to build the thing. You work through scoping decisions, risk methodology choices, control selection and the documentation a certification body will actually ask to see.
By the end you should be able to walk into an organisation with no management system and lead it to a certification-ready state.
How self-paced delivery works
The course is self-paced. You get platform access within 24 hours of enrolment being confirmed, and you keep that access until you have passed your exam; there is no expiry clock forcing you to rush.
Content is delivered as structured video lessons with downloadable reference material, worked examples and quizzes at the end of each module. You sit the PECB exam online at a time you choose.
What you will learn
- Explain the concepts, principles and structure of an ISO/IEC 27001 ISMS
- Plan and lead the implementation of an ISMS against the standard
- Apply a risk management process, including risk assessment and treatment
- Select and justify controls using ISO/IEC 27002 guidance
- Prepare an organisation for a successful certification audit
- Establish monitoring, measurement and continual improvement activities
Course content
1. Introduction to ISO/IEC 27001 and the ISMS
Standards landscape, key definitions, and the management system approach.
2. Planning the implementation
Scope, context, leadership commitment, policy and project governance.
3. Risk assessment and treatment
Asset identification, risk criteria, analysis, evaluation and the statement of applicability.
4. Implementing controls
Organisational, people, physical and technological controls in practice.
5. Monitoring, audit and improvement
Performance evaluation, internal audit, management review and corrective action.
6. Preparing for certification
Evidence, documentation and what a certification body will look for.
Exam and certification
Open-book written exam delivered online through PECB Exams. Multiple sections covering theoretical knowledge and applied scenarios.
Your fee includes your first exam attempt and one free retake within 12 months. After passing, you can apply for the relevant PECB credential.
Related courses
ISO 22301
ISO 22301 Lead Implementer: Business Continuity Management System
- Duration
- 40 hours
- CPD credits
- 31
ISO/IEC 27001:2022 · ISO/IEC 27001:2013
ISO/IEC 27001:2022 Transition
- Duration
- 8 hours
- CPD credits
- 7